Your code stays under your control
Giving an AI agent access to source code should sound alarming. Here is exactly what that access is, and what it is not.
Read-only
It can look, never change.
One app at a time
Never a blanket view.
Every action logged
A complete audit trail.
Fully private option
Runs on your own servers.
What agents get, and what they never get
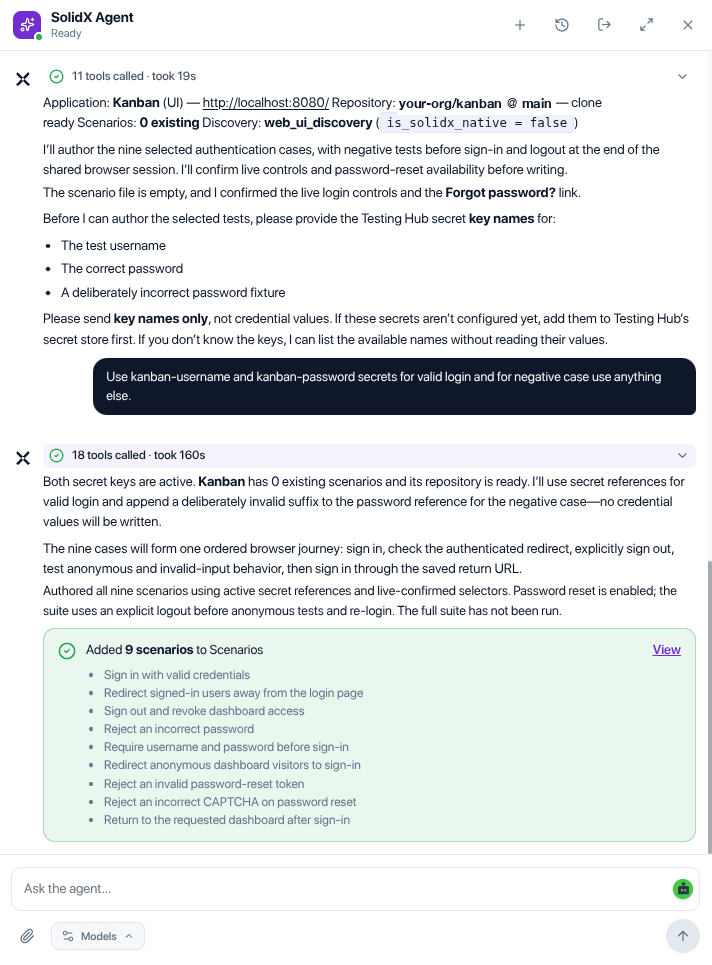
The agent asks for key names, never values
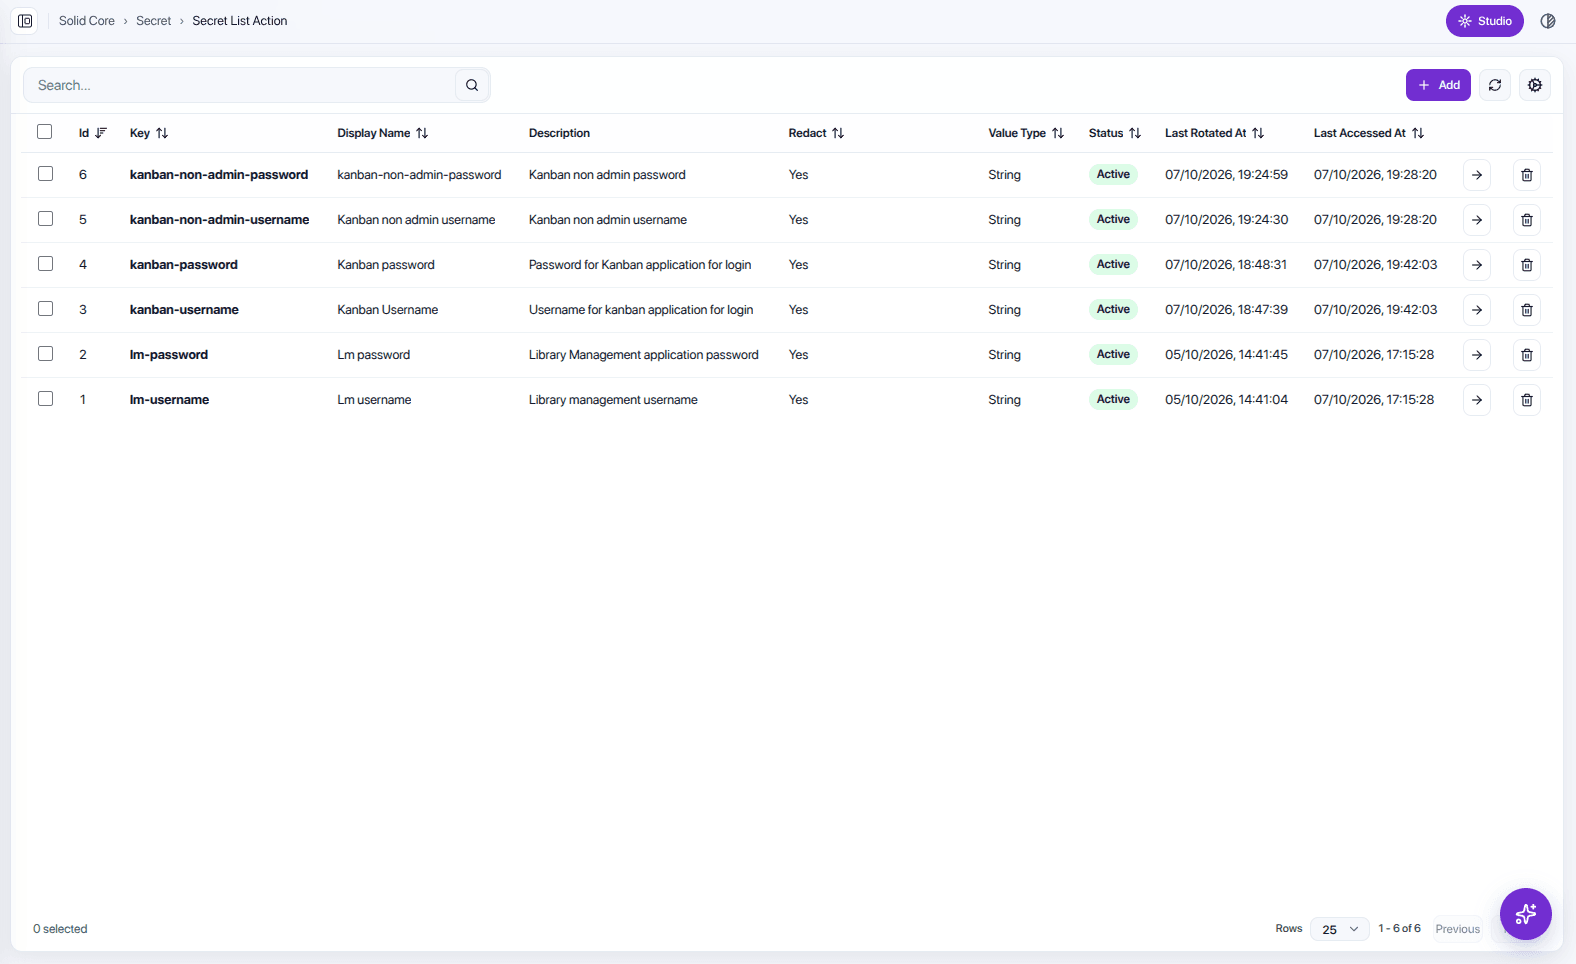
Credentials live in TestHub's secret store, redacted and rotated. Scenarios reference them by name, so no password is ever written into a test.
Encrypted server-side
Git tokens are entered once and never returned to a browser, prompt, or agent.
Secret paths blocked
Known secret files and binaries are excluded from agent reads.
Governed by default
Roles
Editor and Runner roles control who can change and who can run.
Retention
Runs and artifacts purge automatically on your schedule.
Path protection
Every repository path is checked against traversal.
Hosted for you, or on your own servers
Dedicated hosted
A single-tenant instance per customer. Never shared.
Enterprise self-hosted
Your code, tests, artifacts, and scan results never leave your network.
Bring your security team in early
A 30-minute session on the access model, before procurement, not during.