Security checks, included
The same repository connection that powers testing also scans your code. No extra product, no extra bill.
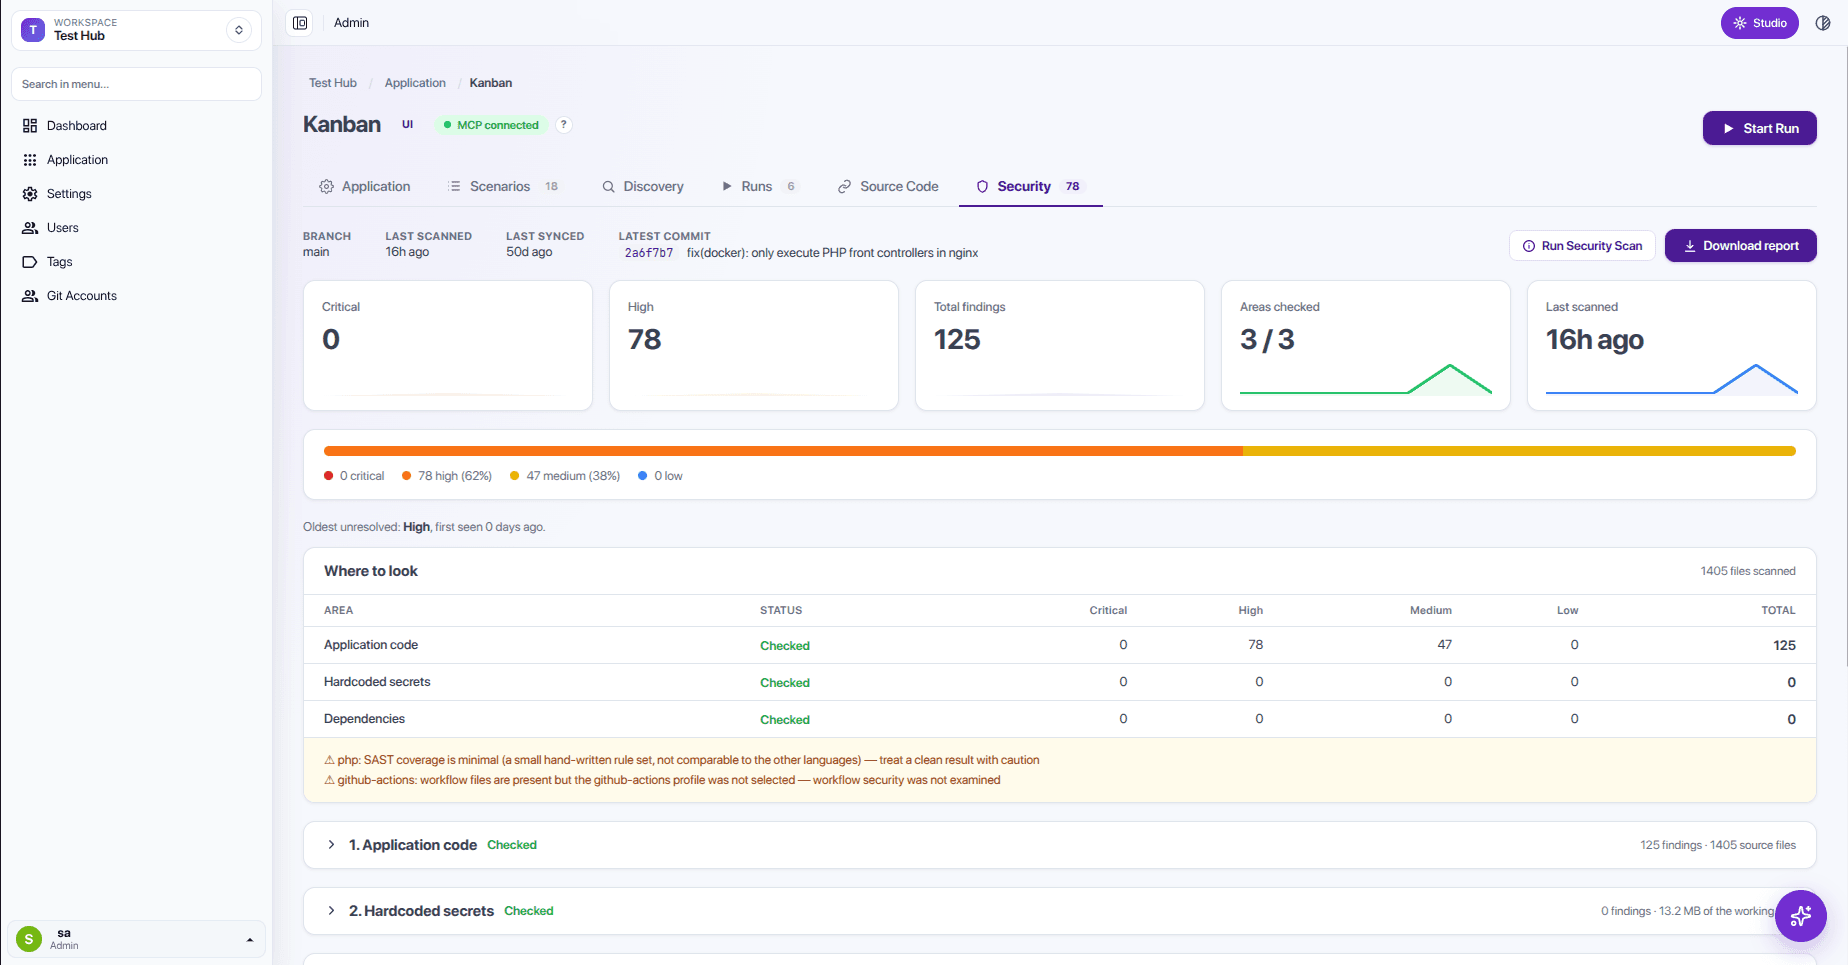
Leaked secrets
Keys, tokens, and passwords committed by accident.
Vulnerable packages
Every dependency checked against public CVE databases.
Risky code
Injection, SSRF, weak crypto, and auth flaws.
Findings you can trust
Deterministic
Same commit and rules, same findings. The LLM is not the scanner.
OWASP-grouped
Mapped to the Top 10. Unmapped findings are kept.
PDF export
Ready for customer security reviews.
AI explains
Summaries and triage sit on top of engine output.
DAST on approved staging URLs
RoadmapIncluding API fuzzing. Never production by default.
PR and MR feedback
RoadmapComments and commit statuses on GitHub and GitLab.
More of TestHub
All features →Scenario Discovery
Reads your code and lists what to test, ranked by risk.
Agentic Authoring
AI drafts the tests. Your team approves every one.
Code Coverage
An honest, route-by-route answer to what is tested.
Recording Studio
Click through a flow once. Get a reusable scenario.
Unblock your next security review
Selling to enterprises? This evidence is what their reviews ask for.